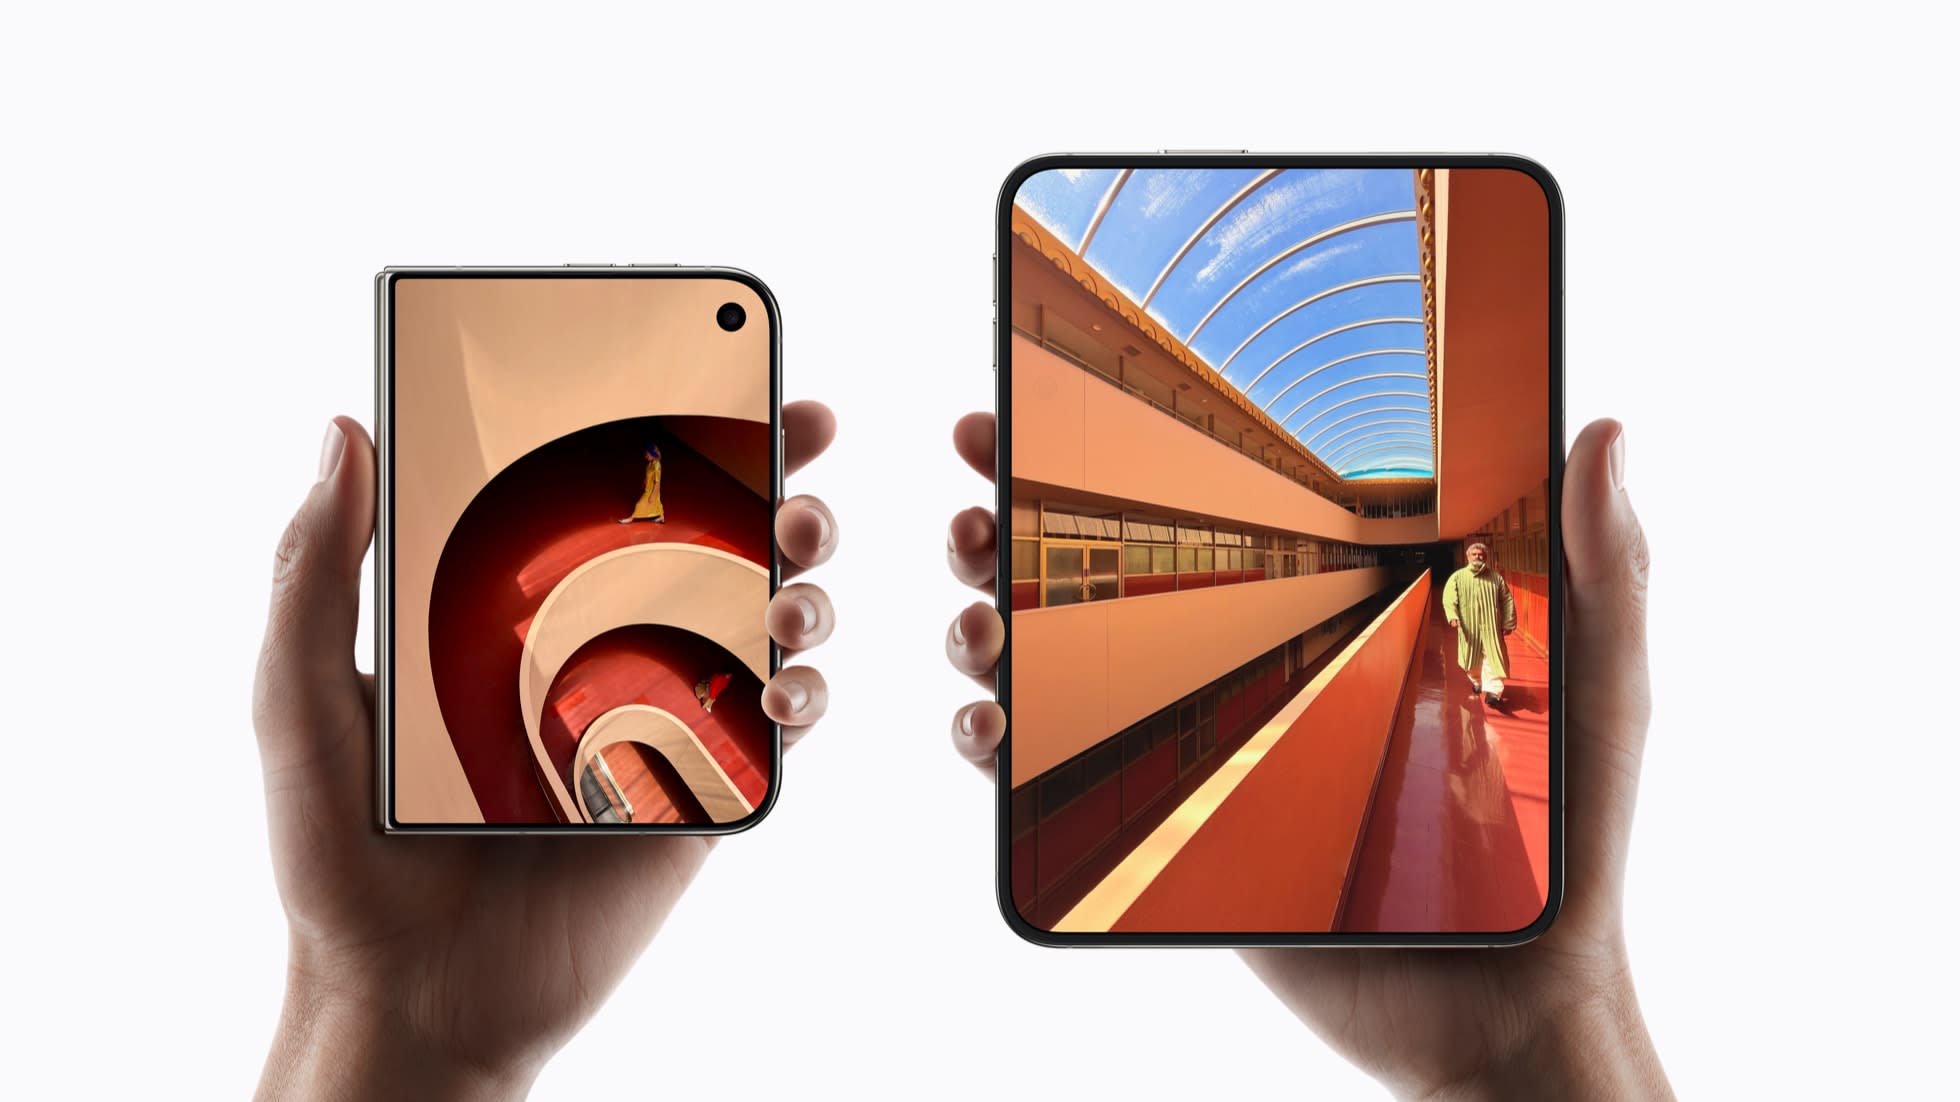
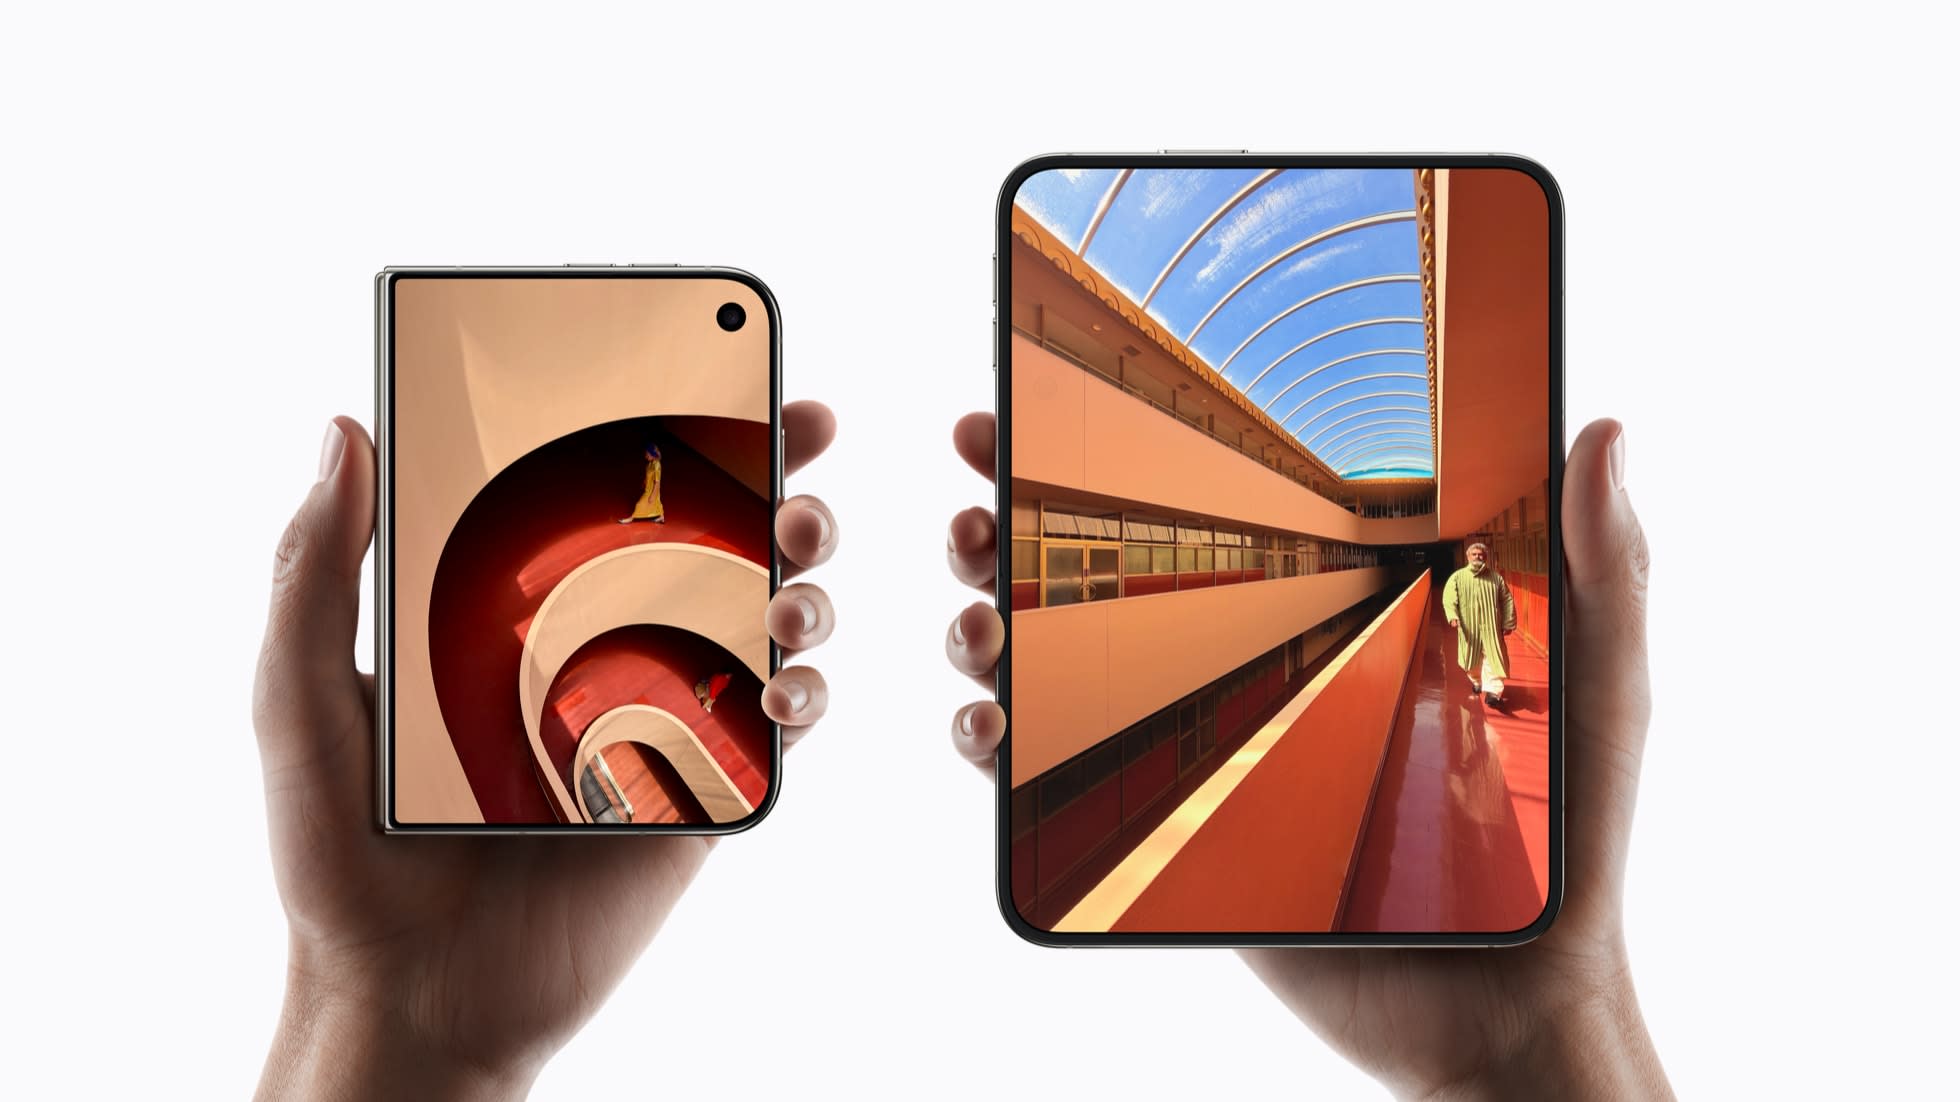
Apple's highly anticipated iPhone Duo has become the latest lure for cybercriminals, with security researchers warning about a fake pre-order website designed to compromise vulnerable iPhones.
According to reports, the fraudulent site imitates Apple's design and promotes an attractive $500 voucher for the foldable iPhone, even though legitimate iPhone Duo pre-orders are not scheduled to begin until October 16.
According to cybersecurity company Malwarebytes, the website is more dangerous than a conventional phishing page. It uses a leaked DarkSword exploit chain that can attempt to compromise certain unpatched iPhones simply when the malicious webpage is opened.
That means victims may not need to enter a password, download an application or even submit the fake pre-order form for the attack to begin.
A fake Apple deal hides a bigger threat
The scam page has been designed to look convincing, using Apple's branding and a countdown designed to create urgency. It asks visitors for basic contact information and presents supposed iPhone Duo configurations.
Researchers found several clues that expose the site as fraudulent. The product specifications and available colors do not match Apple's actual iPhone Duo lineup, while links to policies and other pages do not work properly. The countdown also resets when the page is reloaded.
The timing is another major warning sign.
Apple's official pre-order window for the iPhone Duo has not opened yet. A website claiming to offer an early purchase or discount should therefore be treated with extreme caution.
What can the malware access?
The danger goes well beyond stealing information entered into a fake form.
Malwarebytes found that a successful exploit could give the attackers access to sensitive information stored on a targeted device. The malicious payload attempts to collect device information, installed-app data and Apple Notes, while also searching for cryptocurrency wallets and saved credentials.
Researchers specifically identified attempts to target wallets including MetaMask, Phantom, Trust Wallet, Coinbase Wallet, Exodus and Tonkeeper.
The malware also attempts to access credentials stored in the iPhone's keychain. For anyone who uses an iPhone to manage banking, email, passwords or cryptocurrency, that creates a potentially serious security risk.
How iPhone users can protect themselves
The simplest precaution is to avoid unofficial iPhone Duo pre-order links, particularly advertisements promising unusually large discounts.
Apple recommends treating unexpected requests for passwords, security codes and other sensitive information as potential scams. The company also advises users to contact Apple directly rather than following links supplied through suspicious messages or websites.
Keeping the iPhone updated is equally important. Apple has already issued security updates addressing vulnerabilities associated with the DarkSword exploit chain, making an up-to-date device significantly safer than an older, unpatched version.
Users should also stick to Apple's official website and established retailers when the iPhone Duo pre-order window opens.
For anyone who may already have interacted with the malicious website on an unpatched device, the safest approach is to update the phone immediately and change potentially exposed passwords from a trusted device. Malwarebytes also recommends moving cryptocurrency holdings to a newly created wallet if there is reason to believe wallet information may have been compromised.
Reader Discussion
Join 0 thoughts shared by the communityBe the First to Comment
No discussions started yet. Share your feedback or insights with the TechCrest community!