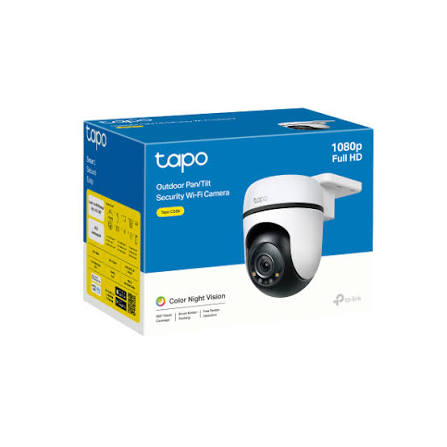
Security researchers at OPSWAT have uncovered two high-severity vulnerabilities in TP-Link’s Tapo smart cameras that could allow attackers on the same local network to bypass authentication or disrupt the devices.
The first flaw, CVE-2026-15315, affects the Tapo C120 V1 and C200 V5 and carries a CVSS score of 8.7.
It could allow an attacker to bypass normal authentication controls and obtain administrative session tokens, potentially gaining access to privileged camera functions.
A second vulnerability, CVE-2026-15316, affects the Tapo C200 V5. Attackers can send oversized encrypted data that may cause the camera to crash or restart, resulting in a temporary denial-of-service condition.
TP-Link released fixes in August. Users of affected models should update their camera firmware to the latest available versions to reduce the risk of exploitation.
Reader Discussion
Join 0 thoughts shared by the communityBe the First to Comment
No discussions started yet. Share your feedback or insights with the TechCrest community!